


Compliance gap analysis
Know where you stand while there’s still time.
EA runs a ready-made workflow for ISO 27001, CSRD, CDP or B Corp, marks each requirement against your own policies and records with the source beside it, and asks the person who holds each gap.
Try EA free. No card needed.

Organisations that run work on EA





Why it starts over each time
Each run picks up where the last one stopped.
Where you stand never stays put. Each audit, renewal, framework revision or new customer requirement means working it out again: someone reads the standard against the shared drive and builds a spreadsheet of what’s covered. By the time it’s finished a policy has been revised and an owner has moved on, and because the spreadsheet holds no link to the evidence, the next one starts from nothing. Gap Analysis keeps the link, so each run starts from the last.
01
No spreadsheet to build first
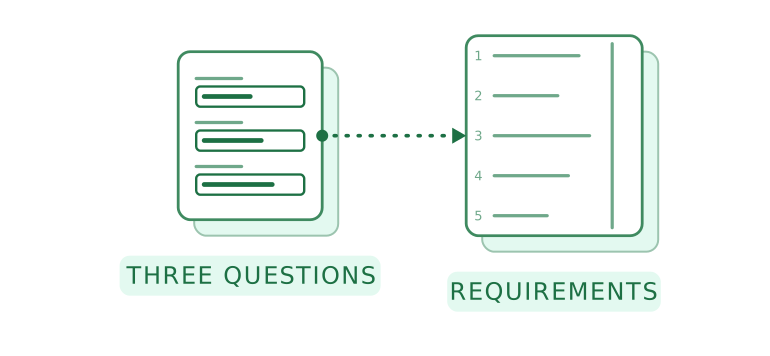
Workflows built by EA’s analysts for ISO 27001, CSRD, CDP and B Corp ask for what they need first, such as scope, sites, sector and your last assessment, then lay out each requirement that applies.
About skills and workflows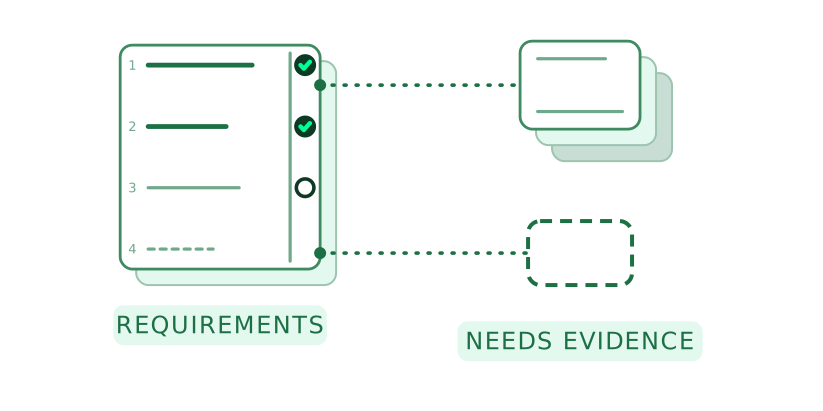
02
Each mark shows its source
Each requirement is matched to the policy, record or approved answer that covers it, shown beside the mark. Evidence that covers part of a requirement is marked partly met; where nothing supports it, EA says so.
About the Knowledge Library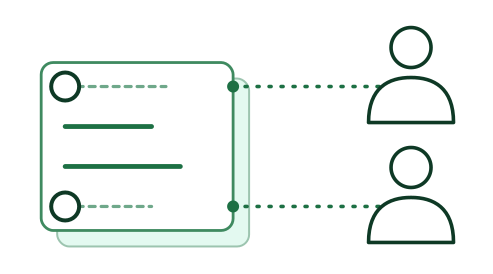
03
Each gap has a name and a date
EA groups the gaps by who holds the evidence and asks each person once, with a date before your audit or deadline. What they send is checked, approved and counted at the next run.
About the agent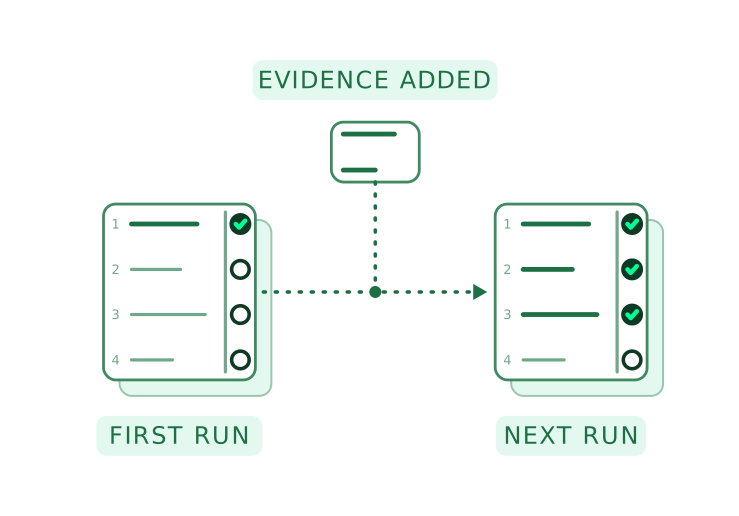
04
The next run starts from this one
Run the analysis again whenever you choose. It starts from the evidence your team has added and approved since, and flags anything that has expired in the meantime.
Worked example
A first ISO 27001 audit, with time to spare.
A software company books its first certification audit for February and runs the ISO 27001 gap analysis in November: clauses 4 to 10 and the 93 controls in Annex A, against the policies and records it already holds.
01 / 04
- EA
Asks for the scope, the sites and the folders to read, then lays out each clause and control with the evidence it expects to see.
Your teamThe Information Security Manager sets the scope and points EA at the policy folder, the risk register and the asset register.
- EA
Marks 58 controls met, 21 partly met and 14 not met, each with the policy or record it relied on, or a note of what’s missing. Knowledge library & memory
Your teamThe Information Security Manager reads the partly met controls beside their sources.
- EA
Groups the gaps by who holds the evidence, IT, HR, facilities, legal and operations, and asks each once, due by 29 January. Agent
Your teamEach owner sends what exists or starts on what doesn’t.
- EA
Takes the analysis for approval, then runs it again in January from the evidence added since, with three controls still open. Approvals & sign off
Your teamThe Information Security Manager approves each run, and the certification body audits in February.
See an ISO 27001 gap analysis run on a company’s own policies and records. EA is ISO 27001 certified, and prepared for its own audit in EA.
Book a demoWhat Gap Analysis does
What you get from each run.
As it reads
- Where your evidence already sits
Upload files, or sync them from SharePoint, OneDrive or selected Google Drive files, in the folders they already sit in.
- Last time counts
Add your previous assessment or submission, and EA reads it against the current requirements, so you see where last year’s answers no longer meet them.
As you close the gaps
- A form you can work in
The result is a requirement-by-requirement form. Reviewers change a mark, comment on it and ask EA to rework the reasoning, as with any other form.
- The start of the response
Once the gaps close, the same evidence drafts the questionnaire, the disclosure or the audit pack, so it’s gathered once.
FAQ
Questions about gap analysis.
What security, sustainability and compliance leads ask before their first run.
Checking each requirement of a framework against the evidence you hold, marking what’s met, partly met or missing, and giving each gap an owner. For ISO 27001 that means clauses 4 to 10 and the 93 Annex A controls; EA matches each to your policies and records, shows the source behind each mark and asks the owner of each gap.
It matches the requirement to a specific policy, record or approved answer and shows that source beside the mark, so a reviewer can check the reasoning. If your screening policy exists but no screening records are on file, control A.6.1 is marked partly met, with the policy as its source and the records as what’s missing.
It tells you what your evidence covers and where it falls short; your certification body, auditor or rater makes the judgement. EA works alongside them and your consultant, and gives all of you the same view of the evidence.
ISO 27001, CSRD, CDP and B Corp. For anything else, such as a customer’s own requirements or a regulator’s template, EA drafts against the document you give it, and the answers it can’t evidence are marked “Needs evidence”.
Work from what you have. Upload the files or connect the drives your team and consultants already use; EA reads them where they are, and a reviewer can point it at more if a control comes back not met.
It depends on the plan your organisation chooses. Plans differ by the number of autofills, the workspaces you need and the size of your knowledge library; see the pricing page.
Yes. Your consultant keeps the advice and the judgement; EA does the reading, the matching and the asking, and both of you work from the same analysis and its sources.


Your next audit, without the spreadsheet.
93 controls marked, for your Information Security Manager.
Related
Once you know the gaps, the rest of EA closes them.
Other modules
- AgentTakes each gap to the colleague who holds the evidence and brings their reply back.
- Knowledge library & memoryHolds the policies and records each requirement is matched against, each with its owner.
- AutofillDrafts the questionnaire or response from the same evidence once the gaps are closed.
- Approvals & sign offTakes the finished analysis to its reviewers and its approver.
By industry
 SoftwareISO 27001 before the first enterprise customer asks for the certificate.
 Healthcare and life sciencesSupplier assessments that expect certified security before you’re approved.
 ConsultingThe certifications clients ask about in vendor due diligence.
 Energy and utilitiesCSRD and CDP readiness, checked against the data you already report.